OT Cybersecurity News: Threat Updates for Industrial Systems in 2026
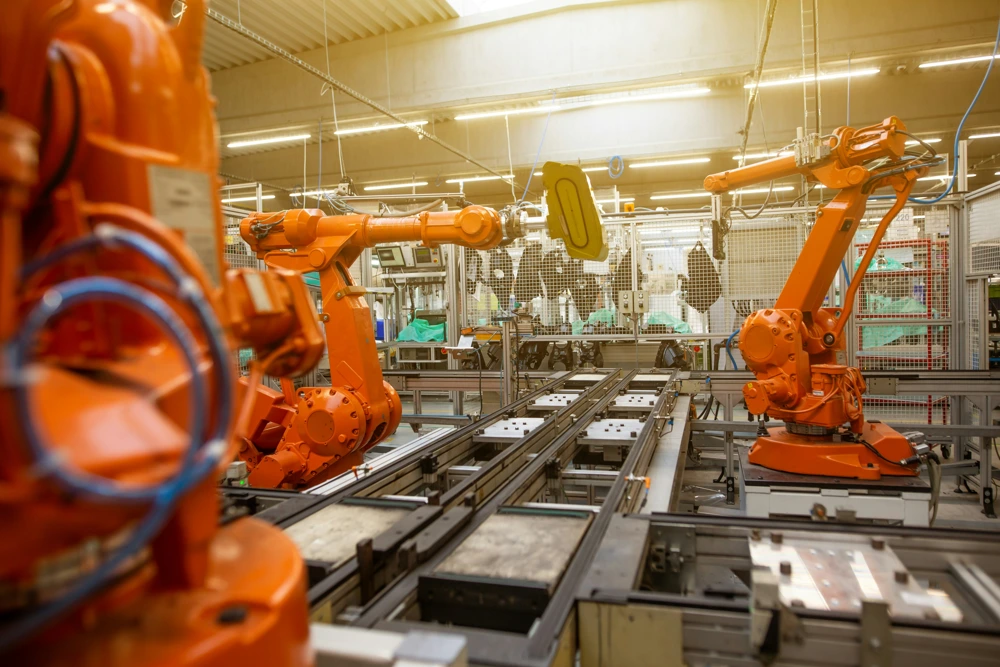
OT cybersecurity news has never been more urgent. Operational technology — the systems that control power grids, water treatment plants, manufacturing lines, and transportation networks — is under sustained assault from criminals, spies, and saboteurs. The consequences of failure here are not just financial; they are physical, affecting the essential services modern life depends on.
This briefing covers the latest OT cybersecurity news: who is attacking industrial systems, how they are getting in, what defenders are doing about it, and where the threat landscape is heading. If your organization operates anything with a programmable logic controller, this is required reading.
The 2026 Threat Landscape for Operational Technology
The defining feature of current OT cybersecurity news is convergence — the merging of IT and OT networks, of criminal and state-sponsored tactics, and of cyber and physical consequences. Attacks that once required nation-state resources can now be executed by ransomware gangs using commodity tools. Meanwhile, state actors have adopted criminal techniques for deniability.
Ransomware remains the most common threat to industrial organizations, though its impact on OT differs from IT. Most ransomware does not directly target control systems; instead, it encrypts business networks, forcing precautionary shutdowns of production as operators lose visibility. The result is the same — halted operations — but the attack path runs through IT, making IT security hygiene directly relevant to OT resilience.
More concerning in recent OT cybersecurity news are intrusions specifically targeting control systems. Threat actors are conducting reconnaissance of industrial networks, harvesting credentials for engineering workstations, and in some cases deploying OT-specific malware. These operations suggest preparation for disruptive attacks, whether for geopolitical coercion, wartime contingency, or criminal extortion.
Threat Actor Categories
Understanding who attacks OT clarifies the OT cybersecurity news. Cybercriminals seek money — through ransomware, extortion, or theft of intellectual property. They are opportunistic, exploiting whatever access they can gain, and their OT impact is often collateral rather than intentional.
State-sponsored actors pursue strategic objectives: intelligence collection, pre-positioning for future conflict, or coercive signaling. They are patient, well-resourced, and specifically interested in OT. Multiple governments maintain dedicated programs for industrial control system intrusion, and OT cybersecurity news regularly documents their activities.
Hacktivists and insiders round out the picture. Politically motivated groups have targeted industrial systems for disruption and publicity. Disgruntled employees or contractors with legitimate access remain a persistent risk, particularly given the specialized knowledge required to cause physical damage.
Ransomware’s Industrial Impact
Several major industrial ransomware incidents feature in 2026’s OT cybersecurity news, illustrating the playbook. Attackers gain initial access through phishing or exposed remote services, establish persistence in the IT network, escalate privileges, and deploy ransomware widely. When business systems encrypt, industrial operators face an impossible choice: continue running blind or shut down safely.
The most prepared organizations have learned to maintain OT visibility during IT outages. Out-of-band monitoring, independent backup systems for critical controls, and practiced manual operation procedures allow continued safe production even when corporate networks are down. This separation — logical and sometimes physical — between IT and OT is the single most important architectural defense.
Recovery from industrial ransomware is slower and more complex than from IT ransomware. Control systems may require vendor involvement to restore. Safety instrumented systems need revalidation. Regulatory notifications add overhead. Organizations that have rehearsed recovery — actually rebuilding systems from backups under time pressure — fare dramatically better than those with untested plans.
State-Sponsored Threats to Critical Infrastructure
The most alarming OT cybersecurity news involves state actors targeting critical infrastructure. Intelligence agencies across multiple countries have publicly warned about intrusions into power, water, transportation, and communications systems by foreign government hackers. These are not theoretical risks; they are documented operations.
The pattern typically involves years of quiet access. Attackers compromise IT networks of infrastructure operators, pivot toward OT environments, learn the industrial processes, and maintain persistence. The purpose may be espionage, but the positioning enables sabotage — the ability to disrupt essential services during a crisis.
Volt Typhoon-style operations, where state actors live off the land using legitimate tools to avoid detection, have become the template. These intrusions are extraordinably difficult to detect because they generate minimal malware signatures. Defenders must hunt for behavioral anomalies: unusual access patterns, unexpected credential use, reconnaissance of control system configurations.
Geopolitical Dimensions
OT cybersecurity news cannot be separated from geopolitics. Tensions between major powers manifest directly in cyberspace, with critical infrastructure as the highest-value target. Smaller nations find themselves caught between larger adversaries, their infrastructure potentially targeted as proxy battlegrounds or collateral damage.
This reality is driving government action worldwide: mandatory incident reporting for critical infrastructure, security requirements for OT operators, information sharing programs, and in some cases, active defense measures. The regulatory burden is growing, but so is government support — funding, intelligence sharing, and incident response assistance.
IT/OT Convergence: The Expanding Attack Surface
The convergence of information technology and operational technology is the structural driver behind much of today’s OT cybersecurity news. Industrial systems once ran on isolated, proprietary networks. Today they run on Ethernet, Windows, and cloud-connected platforms — gaining efficiency and connectivity while inheriting IT’s vulnerabilities.
Remote access is the sharpest edge of convergence. Vendors need remote access for maintenance. Engineers work from home. Corporate analytics pull data from plant floors. Each connection is a potential attack path. The OT cybersecurity news is full of incidents where inadequately secured remote access provided the initial foothold.
Cloud and edge computing in industrial environments add further complexity. Predictive maintenance, digital twins, and AI-driven optimization require data flows between OT and cloud platforms. Securing these flows — authenticating every connection, encrypting every transmission, monitoring every anomaly — is the central architectural challenge of modern OT security.
Securing the Converged Environment
Best practices for converged IT/OT security are well established, though implementation lags. Network segmentation based on the Purdue model or ISA/IEC 62443 zones and conduits limits lateral movement. Unidirectional gateways or data diodes allow monitoring data out while preventing attacks in. Jump servers with multi-factor authentication control remote access.
Asset inventory is foundational. Many organizations discover, during their first serious OT security assessment, devices they did not know existed — legacy controllers, forgotten remote access points, vendor-installed modems. You cannot secure what you do not know you have, making comprehensive discovery the essential first step.
Regulatory Developments: NIS2, TSA Directives, and Global Standards
Regulation features heavily in 2026’s OT cybersecurity news. The EU’s NIS2 directive imposes stringent requirements on essential entities, including risk management measures, incident reporting within 24 hours, and personal liability for management. Enforcement is ramping up, and penalties are substantial.
In the United States, TSA security directives for pipeline and rail operators mandate specific controls: network segmentation, access control, continuous monitoring, and incident response planning. Similar requirements are expanding to other transportation subsectors. The trend is unmistakable — from voluntary guidance to mandatory requirements.
International standards provide the technical backbone. ISA/IEC 62443 remains the definitive framework for industrial automation security, with growing adoption in procurement requirements and insurance underwriting. Organizations aligning to 62443 find regulatory compliance significantly easier, as most new regulations map to its concepts.
Compliance as a Floor, Not a Ceiling
A consistent theme in OT cybersecurity news is that compliance alone is insufficient. Regulations establish minimums, but determined adversaries exceed minimums effortlessly. The organizations that weather real attacks are those that treat compliance as the starting point and build genuine security capability beyond it.
This distinction matters for resource allocation. Money spent purely on compliance documentation produces audit artifacts. Money spent on network monitoring, incident response capability, and workforce development produces resilience. Smart CISOs satisfy auditors while investing primarily in the latter.
Zero Trust for Operational Technology
Zero trust architecture — never trust, always verify — is migrating from IT to OT, generating significant discussion in OT cybersecurity news. The principles translate well: authenticate every device and user, authorize every connection based on policy, continuously verify, assume breach. The implementation, however, must respect OT constraints.
Traditional zero trust tools designed for IT often fail in OT environments. Agents cannot be installed on PLCs. Network scans can crash fragile devices. Authentication prompts interrupt operators during emergencies. Successful OT zero trust implementations adapt the model: passive monitoring instead of active scanning, pre-authenticated emergency access with strong auditing, policy enforcement at network boundaries rather than on endpoints.
Microsegmentation is the most practical zero trust element for OT. Dividing the control network into small zones with strictly controlled conduits contains breaches and makes attacker lateral movement extraordinarily difficult. Combined with comprehensive monitoring of inter-zone traffic, microsegmentation provides most of zero trust’s benefits with manageable complexity.
Threat Detection and Monitoring in OT
Detection capabilities are improving, a bright spot in OT cybersecurity news. OT-specific monitoring platforms now provide deep protocol inspection for industrial protocols — Modbus, DNP3, OPC, PROFINET — detecting anomalous commands, unauthorized configuration changes, and reconnaissance activity that IT security tools miss entirely.
The challenge is operationalizing detection. Alerts must reach people who understand both cybersecurity and industrial processes. A suspicious Modbus command means nothing to a SOC analyst without OT context, and everything to a control engineer who recognizes it as physically dangerous. Bridging this expertise gap — through training, collaboration, or combined teams — determines whether detection investments pay off.
Threat intelligence sharing for OT is maturing. Sector-specific Information Sharing and Analysis Centers, vendor threat reports, and government alerts provide indicators and tactics relevant to industrial environments. Organizations that consume this intelligence and hunt proactively for matching activity catch intrusions that passive defenses miss.
Deception Technology in Industrial Networks
An emerging technique gaining attention in OT cybersecurity news is deception — deploying honeypots that mimic PLCs, HMIs, and engineering workstations. Attackers conducting reconnaissance encounter convincing decoys, revealing their presence while wasting their effort. In OT environments, where legitimate traffic patterns are highly predictable, anomalies stand out clearly against decoys.
Incident Response for Industrial Systems
OT incident response differs fundamentally from IT incident response, a distinction emphasized repeatedly in OT cybersecurity news. In IT, the priority is typically to isolate and eradicate quickly. In OT, hasty isolation can cause physical damage — shutting down a chemical process incorrectly can be more dangerous than the cyberattack itself.
Effective OT incident response requires pre-planned coordination between cybersecurity, operations, engineering, and safety teams. Decision authority must be clear: who can authorize taking a process offline, under what conditions, with what safety verifications. These decisions cannot be improvised during an incident.
Tabletop exercises are the most valuable preparation. Simulating a ransomware attack that spreads toward control systems, with all stakeholders participating, reveals coordination gaps, unclear authorities, and missing procedures. Organizations that exercise regularly respond to real incidents with practiced competence rather than improvisation.
Supply Chain Security for Industrial Systems
Supply chain risk is a growing focus in OT cybersecurity news. Industrial systems incorporate components from global supply chains — controllers, sensors, software, firmware — each a potential vector for compromise. High-profile incidents involving compromised updates have demonstrated the impact.
Software bills of materials (SBOMs) are becoming standard requirements in OT procurement, providing visibility into component origins. Vendor security assessments, secure development attestations, and contractual security requirements are increasingly common. Some operators are diversifying suppliers to avoid single points of failure, though this trades one risk for integration complexity.
The most sophisticated operators are building software supply chain verification into their change management: validating firmware signatures, testing updates in isolated labs before deployment, and maintaining known-good configurations for rapid restoration. These practices slow deployment but dramatically reduce supply chain risk.
Workforce Development: Building OT Security Expertise
The OT security skills gap is acute and widely discussed in OT cybersecurity news. The field requires rare hybrid expertise — understanding both cybersecurity principles and industrial processes. Control engineers rarely have security training; cybersecurity professionals rarely understand physical processes. The intersection is sparsely populated.
Organizations are addressing this through cross-training: teaching security fundamentals to OT engineers and industrial basics to SOC analysts. Dedicated OT security roles are emerging, commanding premium compensation. Academic programs in industrial cybersecurity are expanding, though graduates remain far fewer than demand.
Managed security services for OT are filling gaps for smaller operators. Specialized providers offer OT monitoring, threat hunting, and incident response as services, bringing expertise that individual organizations cannot hire. As with IT managed services, quality varies — but the best providers deliver genuine capability.
OT Cybersecurity News: Looking Ahead to Late 2026 and Beyond
The trajectory in OT cybersecurity news points to intensifying threats met by maturing defenses. State-sponsored intrusions will continue; criminal ransomware will persist; the attack surface will keep expanding with convergence. But defensive capabilities — monitoring, segmentation, response planning, regulation — are improving faster than many expected.
Several developments bear watching. AI-assisted attack tools may soon target OT specifically, automating reconnaissance of industrial networks. Defensive AI will counter, but the asymmetry favors attackers initially. Quantum-resistant cryptography migration will eventually reach OT, though the long device lifecycles make this a decade-long project.
The fundamental equation remains unchanged. Industrial systems underpin civilization — energy, water, food, transportation, manufacturing. Their security is not an IT issue but a societal one. The OT cybersecurity news of 2026 reflects growing recognition of this reality, with resources, regulation, and attention finally beginning to match the stakes. For operators, the mandate is clear: know your assets, segment your networks, monitor continuously, plan for incidents, and treat OT security with the seriousness that critical infrastructure demands.
Case Studies: Lessons From Real OT Incidents
Examining real incidents documented in OT cybersecurity news yields practical lessons. In one widely reported case, a manufacturing company discovered ransomware spreading through its corporate network on a Friday evening. Because the company had previously segmented its OT network with unidirectional gateways, the control systems remained operational throughout the weekend-long IT recovery. Production continued, orders shipped, and the financial impact was a fraction of what it could have been. The investment in segmentation paid for itself many times over in a single incident.
Another case illustrates the opposite. A water utility with flat networks — IT and OT fully interconnected, default credentials on control devices, no monitoring — suffered a breach that gave attackers direct access to treatment processes. The intrusion was discovered only when an operator noticed unexpected setpoint changes. The utility spent months rebuilding trust with regulators and the public, and the remediation cost far exceeded what preventive security would have required.
The pattern across OT cybersecurity news is consistent: preparation determines outcome. Organizations that invested in the fundamentals before an incident recovered quickly. Those that had not faced extended outages, regulatory consequences, and lasting reputational damage.
What Good Looks Like
The best-defended industrial organizations share recognizable characteristics. They maintain comprehensive asset inventories, updated continuously. Their networks are segmented according to ISA/IEC 62443 principles. They monitor OT traffic with protocol-aware tools and staff who understand what they are seeing. They practice incident response with operations teams involved. They manage vendor access tightly. None of this is exotic — it is disciplined execution of established practices.
Building Your OT Security Roadmap
For organizations beginning or accelerating their OT security journey, the OT cybersecurity news suggests a practical sequence. Start with visibility: discover and inventory every OT asset, map network connections, and understand data flows. This foundational work informs everything that follows and often reveals immediate risks worth addressing.
Next, establish basic protections: change default credentials, segment networks, control remote access, and ensure backups exist for critical systems. These steps eliminate the most common attack paths and dramatically improve resilience. Then build detection capabilities: deploy OT monitoring, establish baselines, and develop the expertise to interpret alerts.
Finally, mature toward proactive defense: threat hunting, regular exercises, supply chain security, and continuous improvement driven by lessons learned. This is a multi-year journey, but each phase delivers meaningful risk reduction. The organizations making steady progress along this path are the ones that will define the positive stories in future OT cybersecurity news.